Ransomware is no longer an isolated IT incident. For banking and healthcare organizations across Latin America and the Caribbean, a successful attack can trigger regulatory penalties, operational paralysis, and irreversible reputational damage. In 2025, over 68% of enterprises in the region reported at least one ransomware attempt, with finance and healthcare ranking among the most targeted verticals.
The question is no longer if an organization will be attacked. It is whether the organization can recover within hours—not days.
This article examines how Veeam's data protection architecture enables regulated industries to build ransomware-resilient backup strategies that meet strict recovery objectives while ensuring data sovereignty.
Why Ransomware Targets Banking & Healthcare
Financial institutions and healthcare providers share a common vulnerability: they cannot afford downtime. A bank's digital channels must remain operational 24/7. A hospital's patient data must be accessible without interruption. Attackers know this. It makes them prime targets for double-extortion tactics, where data is both encrypted and exfiltrated.
Traditional backup strategies often fail under these conditions for three reasons:
- Backups are not isolated. If backup repositories reside on the same network as production systems, ransomware can traverse laterally and encrypt both.
- Recovery is slow. Restoring terabytes of data from conventional backup architectures can take days, exceeding the tolerance thresholds of regulated industries.
- Compliance gaps. Without documented immutability and recovery testing, organizations struggle to demonstrate resilience to auditors and regulators.
What Makes a Backup Truly Immutable
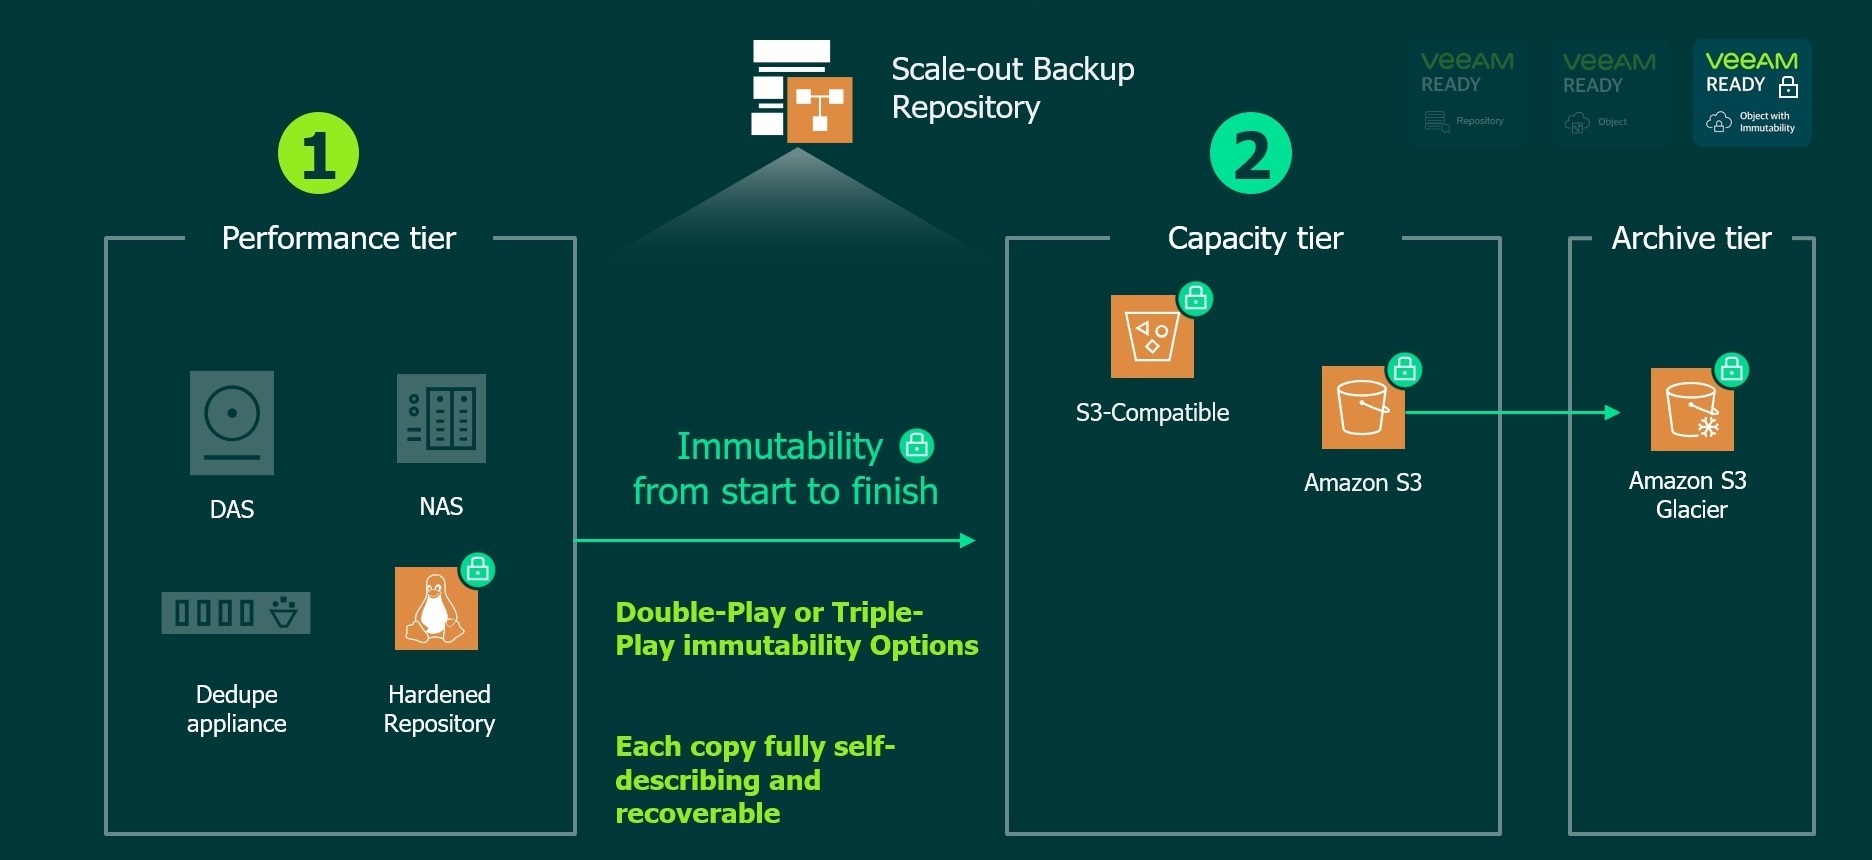
Immutability is the cornerstone of modern ransomware defense. An immutable backup cannot be altered, deleted, or encrypted by any user—including administrators—during a defined retention period.
Veeam implements immutability through hardened Linux repositories, object storage with S3 Object Lock, and air-gapped tape architectures. This ensures that even if an attacker gains full domain access, the backup layer remains untouchable.
Key capabilities include:
- Write-Once-Read-Many (WORM) storage: Prevents overwrite or deletion of backup files.
- Insider threat protection: Eliminates the risk of privileged account compromise affecting backups.
- Automated verification: Regular backup integrity checks confirm that recovery points are valid and corruption-free.
For a comprehensive overview of how Veeam structures immutability across storage tiers, refer to the official Veeam Backup & Replication User Guide on immutability.
Recovery SLAs: From Days to Hours
Recovery Time Objective (RTO) and Recovery Point Objective (RPO) are not abstract metrics. For a Caribbean bank processing cross-border transactions, an RTO of 24 hours can mean millions in lost revenue. For a hospital managing critical care records, any delay risks patient safety.
Veeam addresses this through:
- Instant VM Recovery: Boot virtual machines directly from backup storage while full restoration proceeds in the background.
- Granular file and application restore: Recover individual files, Exchange emails, or SQL databases without restoring entire systems.
- Orchestrated disaster recovery: Automated runbooks execute failover sequences, reducing human error during high-pressure events.
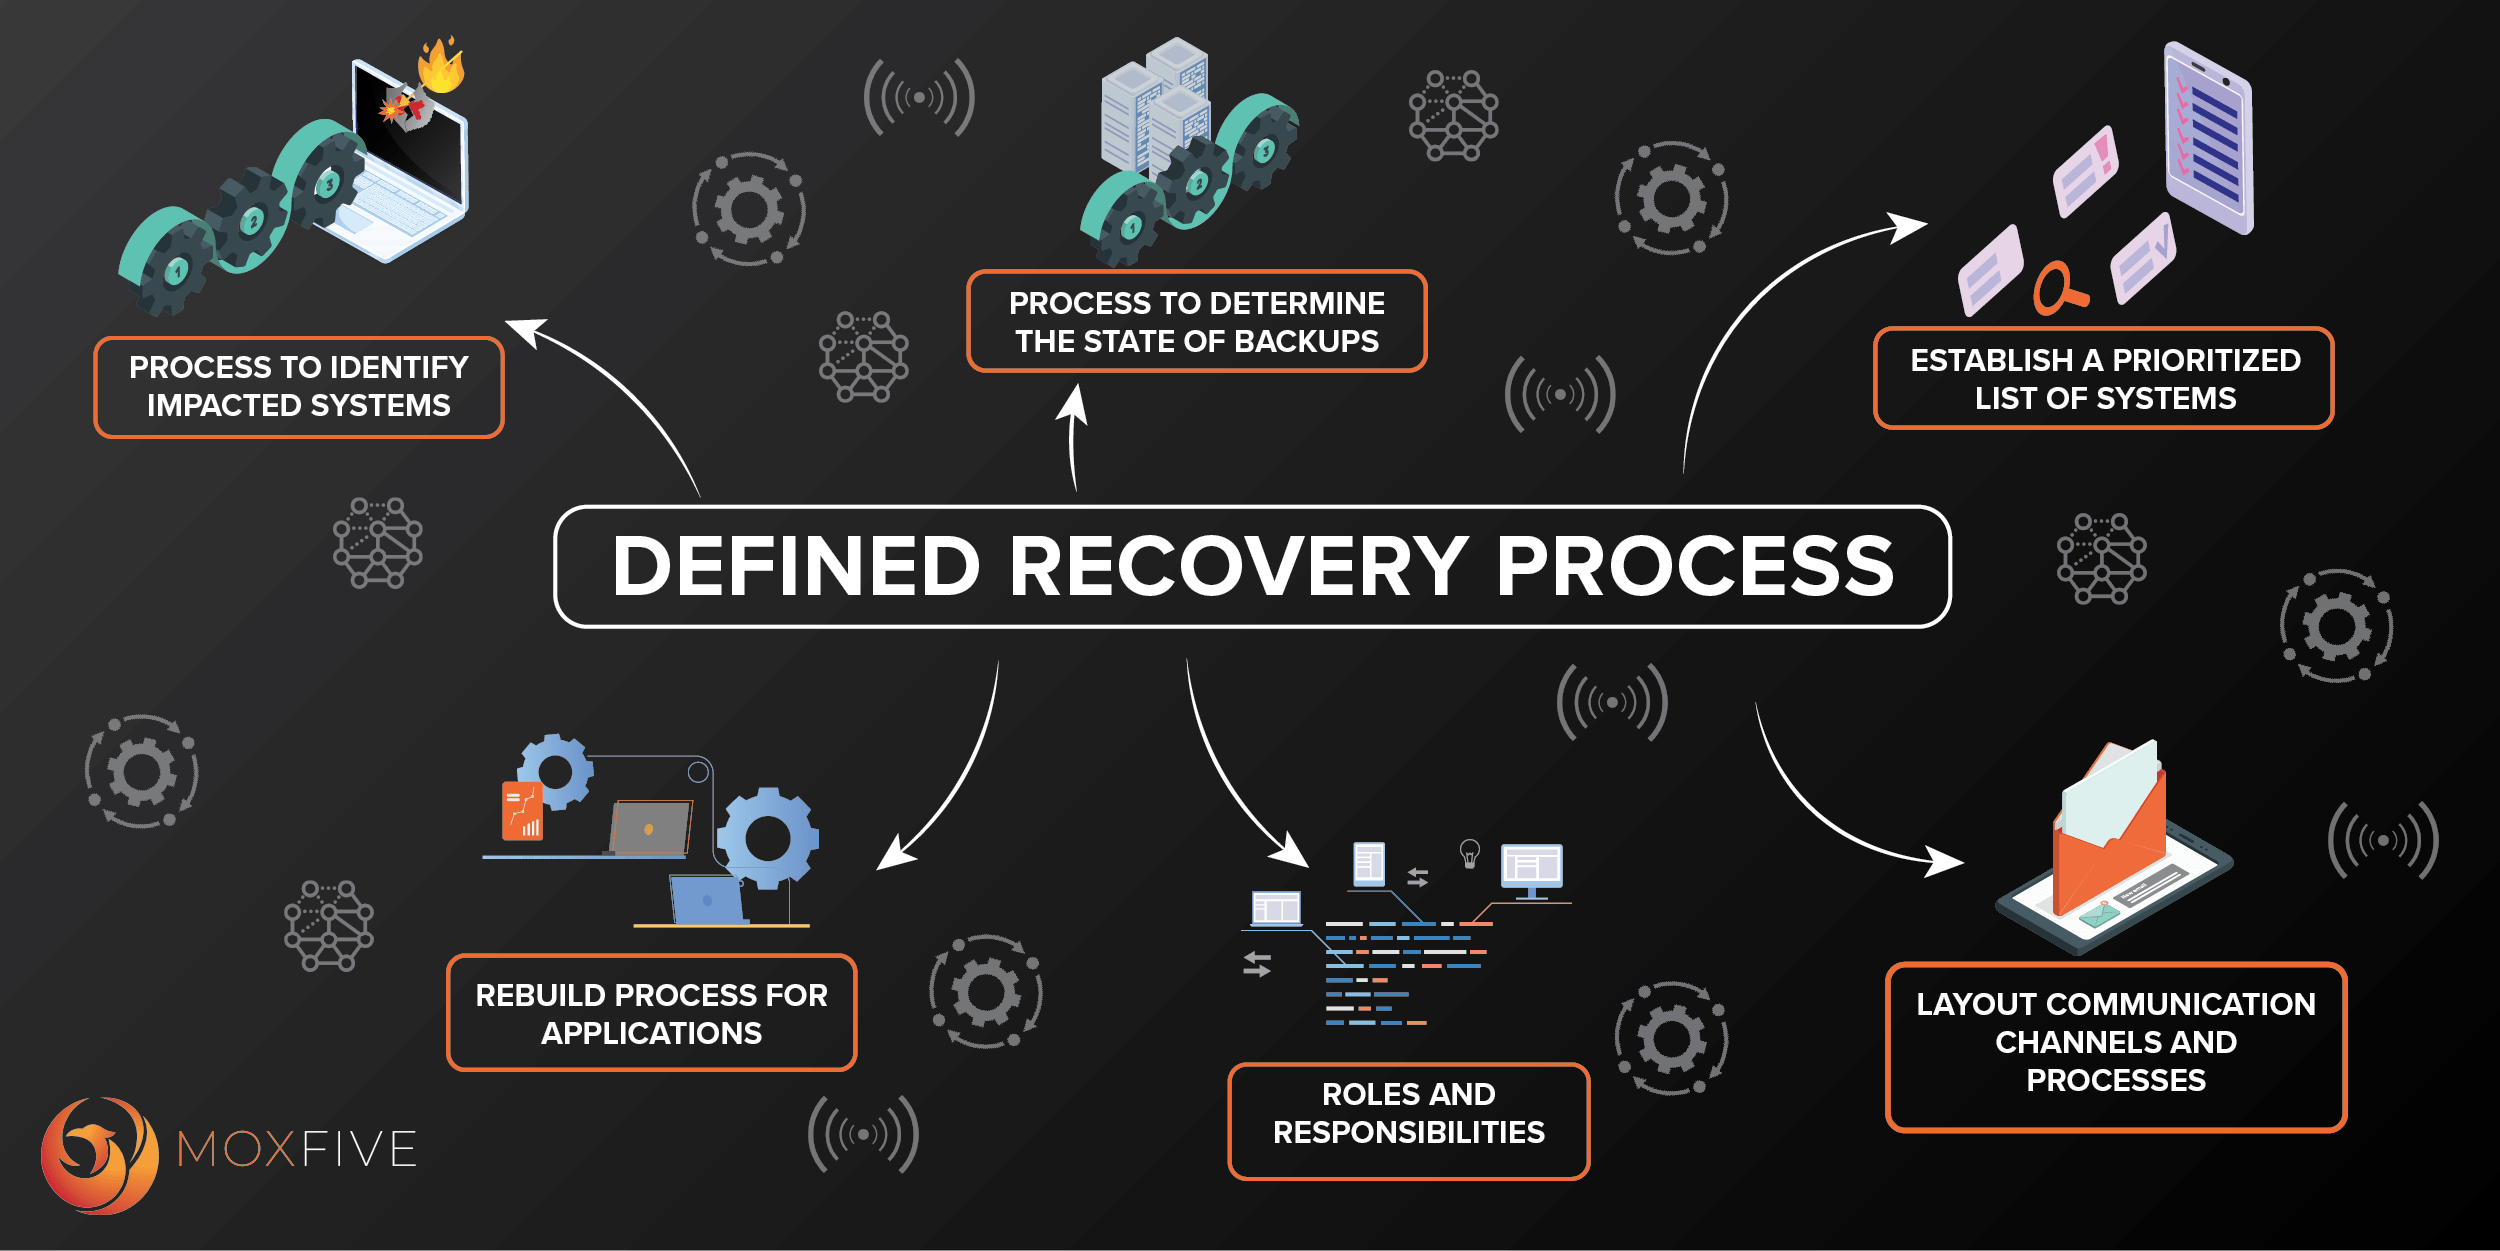
In practical terms, an organization that previously required 48–72 hours to restore 50TB of critical data can now achieve full operational recovery in under four hours.
Compliance & Data Sovereignty in LATAM
Regulatory frameworks across LATAM increasingly mandate data residency, encryption standards, and documented recovery procedures. Veeam supports compliance through:
- Encryption at rest and in transit: AES-256 encryption ensures data confidentiality across all stages.
- Role-based access control (RBAC): Granular permissions align with internal governance and external audit requirements.
- Data sovereignty options: Backups can be retained within national borders, satisfying local regulatory mandates for banking and healthcare data.
Building Your Ransomware Resilience Plan
A resilient backup strategy requires more than technology. It demands process, documentation, and regular validation. Organizations should adopt the following framework:
- Define criticality tiers. Not all data requires the same RTO. Classify systems by business impact.
- Implement the 3-2-1-1-0 rule. Three copies of data, on two different media, one offsite, one immutable, zero errors after recovery verification.
- Test recovery quarterly. A backup that has never been restored is a hypothesis, not a guarantee.
- Document chain of custody. Maintain audit trails for compliance and forensic analysis.
- Engage a certified partner. Veeam-certified architects design, implement, and validate ransomware recovery architectures for regulated industries.
For advanced configurations, Veeam recommends implementing Double-Play or Triple-Play immutability — combining hardened repositories, object storage with Object Lock, and tape archives for maximum resilience.
Conclusion
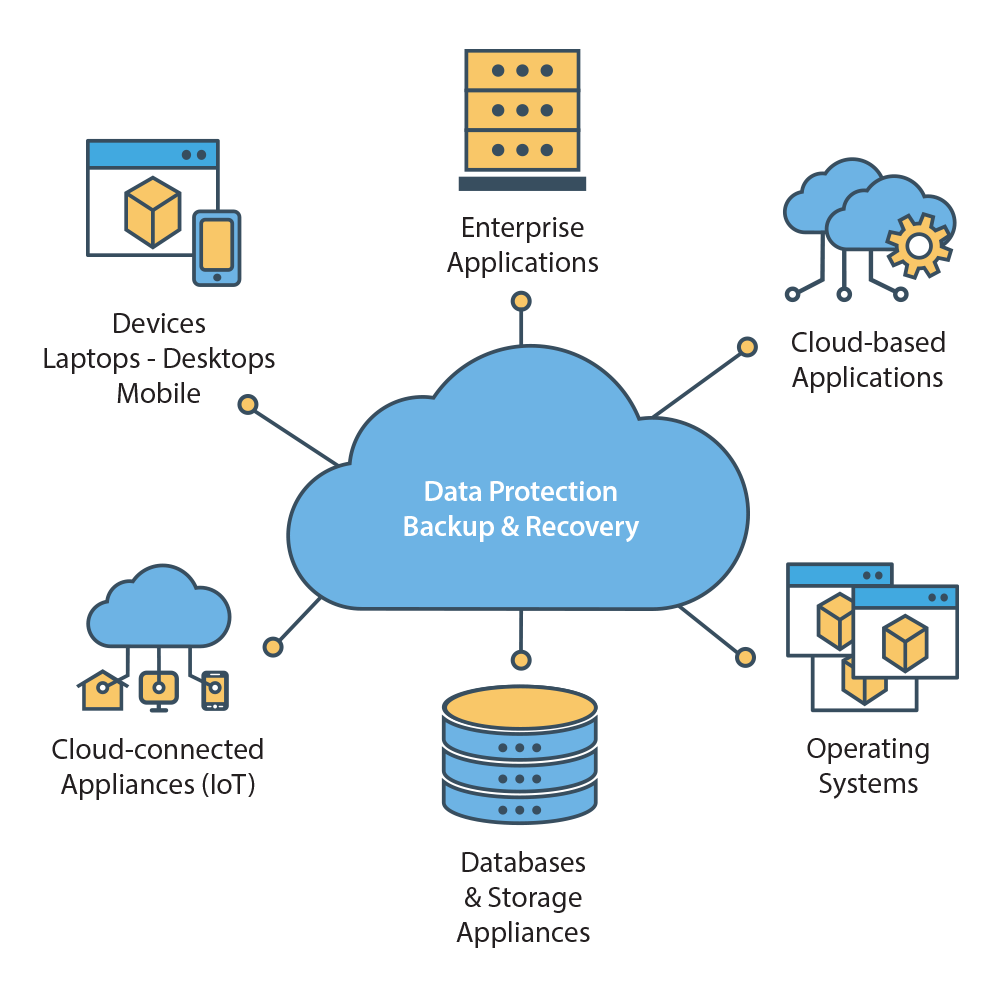
Ransomware resilience is not a product. It is a discipline. For banking and healthcare organizations in LATAM, the combination of immutable backups, rapid recovery orchestration, and compliance-aligned architecture represents the difference between a controlled response and a catastrophic breach.
Veeam provides the technical foundation. The strategic implementation — and the peace of mind that follows — comes from partnering with specialists who understand both the technology and the regulatory landscape of the region.
📋 Download the Complete Ransomware Recovery Framework
Ensure your organization has every critical component in place. This checklist covers backup architecture, immutability configuration, SLA documentation, and compliance readiness — designed specifically for banking and healthcare IT leaders in LATAM.
⬇ Download the 9-Point Ransomware Recovery Checklist
📅 Book a Data Resilience Consultation with V-Corp
Published by V-Corp International — Your Technology Partner Across LATAM & the Caribbean.